Apple Adds an AI Safety Valve to macOS: How New Permission Controls Address Agent Privacy Risks

Apple introduces fine-grained permissions, runtime warnings, and operation transparency records for AI agents in macOS 27.3.
The article introduces Apple's new security mechanism coming with macOS 27.3, centered on addressing privacy risks from AI agents. Traditional macOS privacy relies on app sandboxing plus one-time user authorization, assuming fixed app behavioral boundaries; agents, however, dynamically generate behavioral paths at runtime from natural language instructions, making it hard for users to predict subsequent access at authorization time. Apple's approach is finer-grained authorization, clear warnings at each sensitive access, and recorded agent operation trajectories for retrospective review. Developers must adapt to new APIs and declare intent, while users face more pop-ups and authorization fatigue. Safety guardrails are becoming standard for AI PCs, though whether risks like network requests are covered remains unclear.
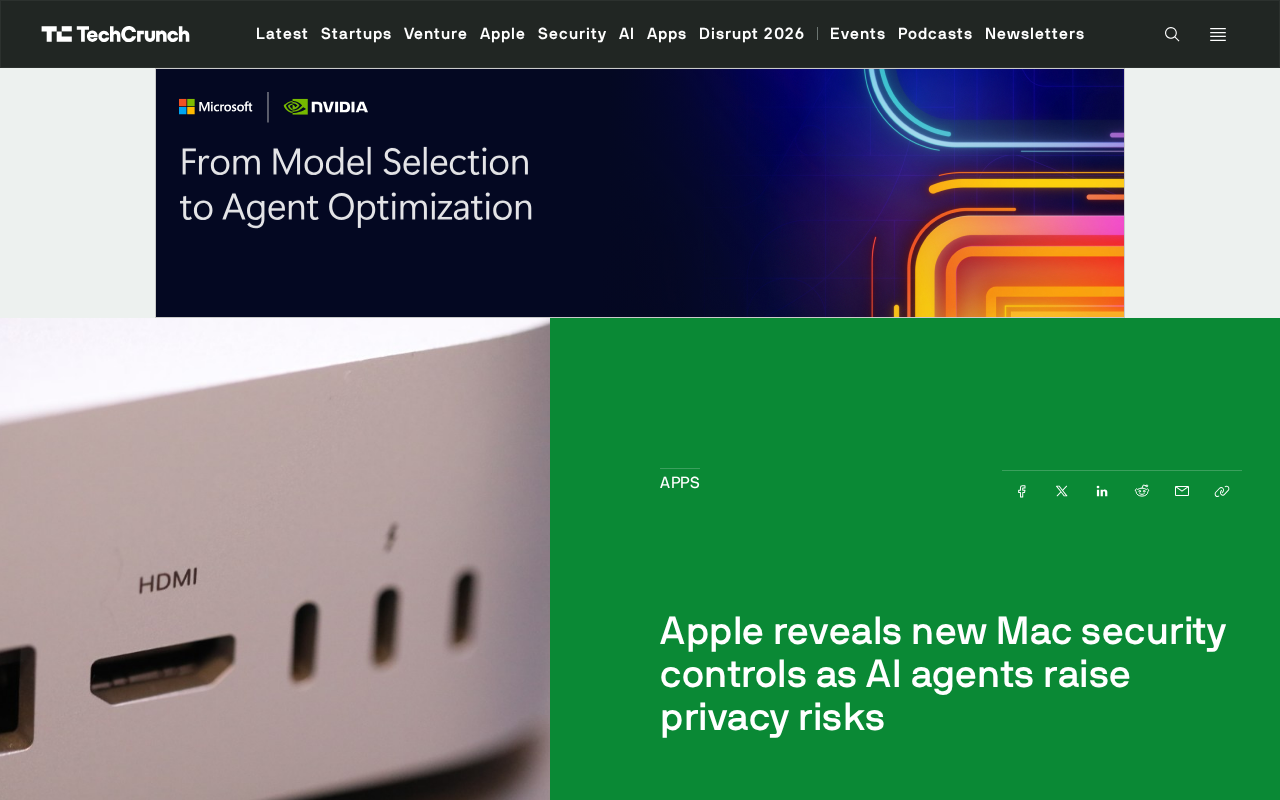
Apple, after teasing the changes in October, has now detailed the new permission controls, warnings, and transparency features coming to macOS 27.3. The core goal of this mechanism is to address the privacy risks posed by AI agents and other apps. When your computer is running agents that can autonomously operate on files, call APIs, and execute tasks across applications, the traditional permission model is clearly no longer sufficient—Apple's answer is: more granular controls, more prominent warnings, and more transparent behavioral records.
Why AI Agents Break macOS's Old Permission Model
Traditional macOS privacy protection is built on "app sandbox + user authorization": for an app to access the camera, microphone, contacts, or disk, it must trigger a system dialog and obtain your click to consent. This logic assumes by default that "an app's behavioral boundary is fixed"—it only does what it was written to do.
But AI agents break this premise. An agent can dynamically decide its next action based on natural language instructions, and within a single session it might read documents, retrieve clipboard contents, invoke external scripts, and modify system settings in sequence. Its behavioral path is not predetermined but generated at runtime. This means users find it difficult to predict, at the moment of authorization, which sensitive data it will touch later. Apple's new controls are designed precisely for this kind of "dynamic permission demand."
App Sandbox is a kernel-level isolation mechanism introduced in macOS since OS X 10.7: each app runs in a restricted container and by default can only access its own data directory; any out-of-bounds access to files, network, or hardware resources must be requested externally through system-provided entitlement interfaces. Together with the TCC (Transparency, Consent, and Control) framework, the system gives users the ability to confirm access to sensitive resources such as the camera, microphone, contacts, and screen recording item by item. The implicit assumption of this design is that "an app's set of behaviors is already determined at compile time," so one-time authorization is enough to cover its entire lifecycle. Agents precisely break this assumption—their behavioral branches unfold only at runtime. The sandbox can constrain "what it can touch," but it cannot predict "what it wants to touch right now," so a gap appears between static authorization and dynamic behavior.
New Permission Controls: Slicing Authorization More Finely
According to information disclosed by Apple, macOS 27.3 will introduce more granular permission categories, allowing users to control item by item the resources an AI agent can access rather than simply granting blanket approval. The system will trigger new warning prompts when an agent attempts to access sensitive areas and clearly inform users which app is requesting access, in what manner, and to what scope.
Transparency features are another main thread. The system will record and display the trajectory of sensitive operations related to agents, allowing users to retrospectively review "what it did." This is crucial for troubleshooting anomalous behavior and determining whether a given agent has overstepped. Apple's approach can be summarized as: since it is impossible to exhaustively enumerate all of an agent's behaviors in advance, distribute control points across every sensitive access at runtime and retain auditable records.
TCC (Transparency, Consent, and Control) is the system daemon in macOS responsible for privacy authorization. All pop-ups asking "whether to allow access to the camera/microphone/files" are uniformly adjudicated by it, and users' decisions are persistently recorded. A key point in understanding it is that TCC authorization is usually keyed by "app—resource category"; once the user clicks allow, subsequent access of the same kind is not asked again until the user manually revokes it in System Settings. This is exactly the underlying implementation of the "request once, available globally" model mentioned in the article. The granular controls Apple is introducing this time can be understood as adding more dimensions to this key-value model—for example, splitting "disk access" into authorization by directory or by session, and changing long-lived permissions into revocable, time-limited runtime permissions. For teams developing agent applications, this means they need to move from relying on one-time TCC authorization to proactively calling new permission APIs that can be requested in batches.
What It Means for Developers and Users
For developers, adapting to the new permission APIs means agent-type applications need to declare their access intent more explicitly and handle partial authorization or denial that users may give at runtime. The old "request once, available globally" model will be squeezed. In the short term this increases adaptation costs, but in the long term it helps build user trust in AI applications—after all, no one wants to invite onto their computer an agent that can read and write files across the entire disk.
For ordinary users, the most intuitive change is more pop-ups and clearer prompts. This may bring some "authorization fatigue," but Apple clearly believes that at a stage when AI agent capabilities are rapidly expanding, it is better to ask one more question than to regret it later. The transparency panel provides a remedy channel: even if you clicked agree at the time, you can later verify what actually happened.
Industry Signal: Safety Guardrails Are Becoming Standard for AI PCs
Apple's move is not an isolated event. As on-device AI and agent-form applications increase, operating-system-level safety guardrails are shifting from "optional" to "mandatory." This set of features in macOS 27.3 essentially draws boundaries for AI behavior at the system level, transferring part of the responsibility from application developers to the platform side.
The limitations of this approach are also obvious: the effectiveness of permission controls depends on whether users understand the meaning of the pop-ups, and whether transparency records can be effectively used by ordinary users remains unknown. More importantly, the risks of agents come not only from local resource access but also from network requests and third-party service calls they initiate on behalf of users. Whether this part can be constrained with equal force is not yet fully covered by the information Apple has disclosed.
What is certain is that when AI agents truly begin to "take action" on personal computers, the operating system must evolve from "managing applications" to "managing behavior." macOS 27.3 is a substantive step by Apple on this path, and subsequent evolution deserves continued observation.
On-device AI refers to model inference running directly on the user's local device rather than in the cloud, driven by latency, privacy, and offline availability. For operating systems, the security challenges brought by on-device AI differ fundamentally from the cloud model: the data boundary of cloud services is defined by the provider's domain of responsibility, whereas on-device agents directly hold local resource access capabilities equivalent to those of the user themselves—the files they can open, the scripts they can invoke, and the clipboard they can read are no different from manual user operations. Therefore, platform providers can no longer rely on the premise that "the application itself is trustworthy" and can only push constraints down to the behavioral layer. This is also why the industry regards operating-system-level permission layering, behavior auditing, and runtime alerts as key features distinguishing AI PCs from traditional PCs: computing power is no longer the only selling point; whether agents can safely "take action" is what matters.
One-line Summary
Apple introduces fine-grained permissions, runtime warnings, and operation transparency records for AI agents in macOS 27.3.
Paragraph Summary
The article introduces the new security mechanism Apple is about to launch with macOS 27.3, whose core is addressing the privacy risks brought by AI agents. The traditional macOS privacy model relies on app sandboxing plus one-time user authorization, assuming by default that app behavioral boundaries are fixed; but agents dynamically generate behavioral paths at runtime based on natural language instructions, making it difficult for users to predict at the moment of authorization the scope of subsequent access. Apple's approach is to slice authorization more finely, trigger clear warnings at each sensitive access, and record agent operation trajectories for retrospective review. The article argues that developers need to adapt to new APIs, clearly declare access intent, and handle partial authorization, while users will face more pop-ups and authorization fatigue. Finally, it points out that safety guardrails are becoming standard for AI PCs, but whether risk surfaces such as network requests are covered remains unclear.
Related articles

US AI Secrets Are Leaking: Security Breaches Are Scarier Than Chinese Spies
Vox analysis reveals US AI companies like Nvidia, OpenAI, and Anthropic suffer frequent security breaches—from CEO scandals to internal systems breached in hours—while 'anti-China' info controls mask basic security failures and jeopardize their tech lead.
Azure HorizonDB + VS Code: A New Workbench for AI App Development
Azure Horizon DB is Microsoft's enterprise-grade Postgres service with deep VS Code integration: GitHub Copilot writes SQL, visual query plans, built-in vector indexes and AI models—database ops and AI app development in one workbench.
Black Friday PS5 Game Sale: Major Titles Slashed
Black Friday sales start early with steep PS5 game discounts and deals on controllers and headsets. We break down the sale, top picks, and buying tips.