Malicious Claude Code Extension Infiltrates Cursor: Version 2.1.313 Self-Check and Cleanup Guide

A malicious Claude Code build 2.1.313 appeared in the Cursor extension marketplace, affecting up to 5,000 developers over about 11 hours.
Cursor officially confirmed that a malicious Claude Code extension build (version 2.1.313), not developed by Anthropic, was listed in its extension marketplace for about 11 hours and affected up to 5,000 users. StepSecurity analysis shows that the extension executes immediately on load, collects system information, git email, and environment variable names, and attempts to add the attacker's SSH key, open a reverse tunnel, and set up persistence mechanisms. Although the extension has been removed and the attacker's server has been taken offline, uninstalling may not be enough to remove persistence traces such as the "SVC telemetry key." The article provides self-check steps: confirm the version, check for persistence items, run the official cleanup script, upgrade to a clean version, and rotate tokens from a trusted device. It also points out that the incident exposed shortcomings in distribution trust and supply chain security in the AI programming tool extension marketplace.
Developers using the Cursor editor need to check one version number immediately: 2.1.313. Cursor officially confirmed that a malicious Claude Code extension build, not developed by Anthropic, existed in its extension marketplace for about 11 hours, dated to October 29, affecting up to 5,000 users. The extension has been removed and the attacker's server has been taken offline, but analysis by security firm StepSecurity shows that uninstalling the extension may not be enough to remove all traces.
Incident Recap: A Supply Chain Risk Triggered by a Single Version Number
According to Cursor's official statement, the problematic build appeared in its extension marketplace and was not developed or authorized by Anthropic. This means the attacker somehow mixed a counterfeit or tampered extension package into the official distribution channel, exploiting developers' trust in the name "Claude Code" to complete the deployment.
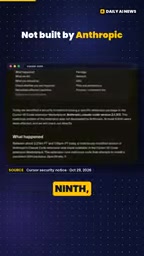
StepSecurity further pointed out that the malicious code executes immediately when the extension loads, without requiring the user to actively trigger any function. This "plug-and-play" attack method greatly shortens the time window from installation to compromise and also makes it difficult to prevent solely by observing behavior.
Breaking Down the Malicious Behavior: What It Actually Did
According to details disclosed by StepSecurity, after running, the extension performed a series of reconnaissance and persistence operations:
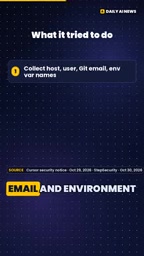
- Collected detailed system information
- Read the user's git email address
- Enumerated environment variable names
- Attempted to add an attacker-controlled SSH key
- Opened a reverse tunnel
- Set up auxiliary persistence mechanisms
Combined, these behaviors point to a typical development environment intrusion chain: first gather host and identity information, then establish a remote access channel through SSH keys and a reverse tunnel, paving the way for subsequent lateral movement or data theft. The collection of git email and environment variable names is especially worthy of vigilance—the former can be used for identity correlation, while the latter may expose name clues for sensitive configurations such as cloud credentials and API keys.
Why Uninstalling May Not Be Enough
Cursor has removed the extension from the marketplace, and the attacker's server is also offline. But StepSecurity warns that simply uninstalling the extension may not be enough to remove the persistence traces left by the attacker.
The report specifically mentions an item called "SVC telemetry key" that needs to be checked. Such naming often disguises itself as a system or telemetry component and is easily overlooked in routine inspections. If this key value is written into system configuration, even if the extension itself is deleted, the attacker may still retain some form of access capability or information exfiltration channel.
Reverse Tunnel is a technology in which an internal network host actively initiates a connection to an external server, thereby bypassing firewall and NAT restrictions to establish a remote access channel. Unlike the conventional "external active connection to internal network," a reverse tunnel is initiated by the controlled endpoint, so to the target network it looks like an outbound connection and is easily overlooked by firewall inspection. Attackers often embed reverse tunnel components in malware to establish a stable channel between the victim host and a C2 (command and control) server for remote command execution, file transfer, or lateral movement within the internal network. In this incident, the extension attempted to open a reverse tunnel, meaning the attacker may already have the ability to directly operate the affected developer's machine from the outside without waiting for the user to actively trigger anything.
Persistence is a key link in the attack chain, referring to the mechanism an attacker establishes on the target system so that even if the initial entry point (such as a malicious extension) is removed or the system restarts, their access capability remains. Common methods include writing startup items, registry keys, scheduled tasks, system services, or tampering with auto-load items in configuration files. The "SVC telemetry key" mentioned by StepSecurity falls into this category: it disguises itself as a system telemetry component and may be written into configuration files or the registry, thereby continuing to take effect after the extension is uninstalled. Detecting persistence requires systematically auditing startup items, service lists, and anomalous configuration keys, rather than relying solely on uninstall operations.
Self-Check and Cleanup Steps
Based on recommendations from Cursor and StepSecurity, affected or potentially affected users should proceed in the following order:
- Confirm the version: Check whether the version number of the Claude Code extension in Cursor is 2.1.313, and if so, remove it immediately.
- Check for the SVC telemetry key: Investigate whether this persistence item exists on the system, and if found, remove it according to security procedures.
- Run Cursor's official cleanup script: Use the cleanup script provided by Cursor to handle residual configuration.
- Upgrade to a clean version: Ensure that an officially confirmed problem-free version is installed.
- Rotate tokens: From a trusted device, replace all credentials that may have been exposed, including code hosting platform tokens, cloud service keys, and more.
Step 5 is easy to underestimate. Considering that the malicious extension had access to environment variable names and git identity information, the attacker already has a basis for targeted guessing or further phishing. Rotating tokens is a necessary action to move from "stopping the bleeding" to "restoring trust." Operating from a trusted device is intended to avoid completing credential updates on a machine that may still be controlled, which could cause the new tokens to be leaked again.
Implications for the AI Programming Tool Ecosystem
The core of this incident is not Claude Code itself, but the distribution trust model of the extension marketplace. As AI programming assistants become the entry point for developers' daily work, their plugin systems effectively hold permissions similar to those of an IDE. A malicious build listed for 11 hours was able to reach thousands of developers, showing that there is still room to strengthen marketplace review, build provenance, and publisher identity verification.
For developers, feasible habits include: paying attention to the publisher and build source of extensions, staying sensitive to sudden version number changes, limiting automatic extension updates in CI or sensitive projects, and regularly auditing credentials stored in environment variables. While AI tools bring efficiency, they also move the entry point for supply chain attacks forward into the editor itself.
The attacker's server is currently offline, and Cursor has completed the removal action. However, the aftermath of a security incident is often longer than the outbreak period. Developers who have used this extension are advised to complete the above self-check and token rotation within this week.
Supply Chain Attack refers to an attacker not directly attacking the final target, but indirectly achieving the goal by compromising third-party components, distribution channels, or development tools it depends on. In the software field, typical forms include tampering with open source packages, hijacking update servers, and impersonating official publishers. In this incident, the attacker mixed a malicious build into the Cursor extension marketplace and exploited developers' trust in the name "Claude Code" and the official marketplace to complete the deployment, which is a typical variant of a supply chain attack. The danger of such attacks lies in the fact that victims actively install and trust components distributed through "legitimate" channels, traditional perimeter defense is difficult to intercept, and the scope of impact may expand rapidly with the scale of distribution.
One-line Summary
A malicious Claude Code build 2.1.313 appeared in the Cursor extension marketplace, affecting up to 5,000 developers over about 11 hours.
Paragraph Summary
Cursor officially confirmed that a malicious Claude Code extension build (version 2.1.313), not developed by Anthropic, was listed in its extension marketplace for about 11 hours and affected up to 5,000 users. StepSecurity analysis shows that the extension executes immediately on load, collects system information, git email, and environment variable names, and attempts to add the attacker's SSH key, open a reverse tunnel, and set up persistence mechanisms. Although the extension has been removed and the attacker's server has been taken offline, uninstalling may not be enough to remove persistence traces such as the "SVC telemetry key." The article provides self-check steps: confirm the version, check for persistence items, run the official cleanup script, upgrade to a clean version, and rotate tokens from a trusted device. It also points out that the incident exposed shortcomings in distribution trust and supply chain security in the AI programming tool extension marketplace.
Related articles

VERS: Editing Activation Explanations to Halve Reasoning Model Tokens
VERS guides reasoning models by editing activation explanations, cutting 45.8% of tokens on GSM8K with only a 0.82 pp accuracy drop and transferring to larger models, but losing accuracy on competition problems.

Finding Errors Is Not Enough: Selective Model Escalation for Entity-Targeted Sentiment Analysis
This study explores selective model escalation for entity-targeted sentiment analysis, comparing data collection ordering, uncertainty-driven re-examination, and model routing—finding that minority-class priority only helps at very small data volumes, the oracle upper bound far exceeds actual gains, and escalation must be tailored to each dataset.

WAS-PO: Using Whitened Advantages to Solve the Correlation Trap in Multi-Reward Reinforcement Learning
WAS-PO paper proposes whitening advantages to correct correlation bias in multi-reward RL: when rewards are correlated, naive weighted summation effectively applies Σ^{1/2}w instead of w. Experiments show training reward improves steadily, but held-out accuracy does not improve in sync, and under two rewards it actually falls behind.