Breaking Edge with Logic Bugs Alone: Analyzing a Microsoft Browser Full-Chain Attack
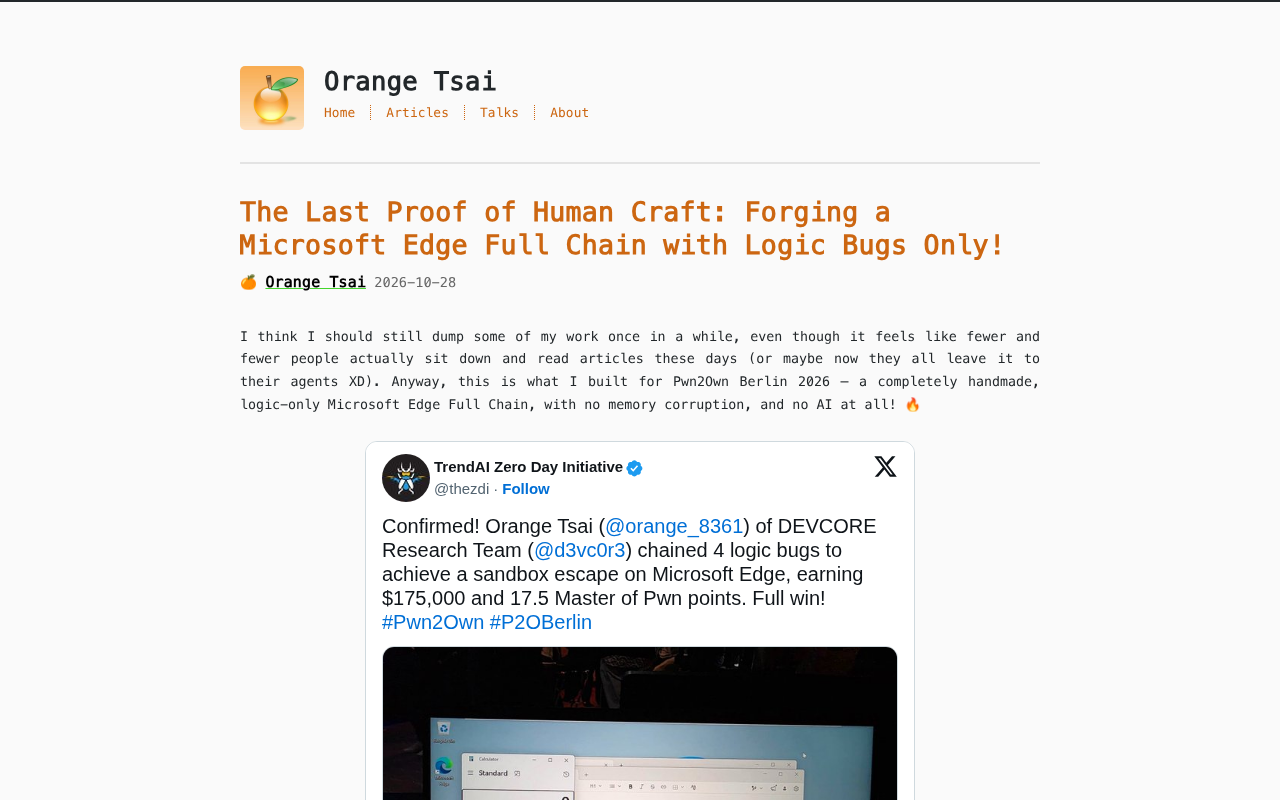
Research explores building a complete attack chain against Edge using only logic bugs and its defensive implications.
The article discusses the Hacker News topic "Forging a Microsoft Edge Full Chain with Logic Bugs Only," analyzing the approach of building a complete browser attack chain relying solely on logic bugs. Unlike memory corruption vulnerabilities such as buffer overflows and use-after-free, logic bugs exploit design flaws in business logic, permission checks, or state management, do not depend on specific memory layouts, can bypass modern mitigations like ASLR, CFG, and sandboxing, and may offer higher exploitation reliability. "Full chain" means starting from the renderer process, breaching process isolation and sandbox boundaries layer by layer, and ultimately affecting the operating system. The article notes that this topic has drawn attention in the security community, reflecting rising interest in non-memory attack surfaces; for vendors, fixing logic vulnerabilities often involves functional refactoring, making cost and priority assessment more complex, and defenders need to incorporate logic validation, cross-process permission boundaries, and state machine consistency into threat modeling. Since the original material only provides the title and source, the analysis remains at the methodological level.
When Logic Bugs Take Center Stage in an Attack Chain
In browser security, memory corruption vulnerabilities have long occupied the spotlight, but a different attack approach is gaining attention: building a complete attack chain relying entirely on logic bugs. A technical analysis from Hacker News (originally titled "Forging a Microsoft Edge Full Chain with Logic Bugs Only") demonstrates this possibility against Microsoft Edge, sparking discussion in the security community.
Unlike classic memory flaws such as buffer overflows and use-after-free, logic vulnerabilities exploit design flaws in business logic, permission checks, or state management. These vulnerabilities often do not depend on a specific memory layout and may be more reliable on browsers with modern mitigations enabled.
Why "Pure Logic" Attack Chains Deserve Attention
The Value of Bypassing Memory Mitigations
Modern browsers universally deploy multiple layers of protection such as ASLR, CFG, and sandboxing, greatly raising the bar for exploiting memory corruption vulnerabilities. Logic bugs can bypass these mechanisms directly—attackers don't need to construct ROP chains or heap sprays, but instead achieve their goals through a series of seemingly legitimate operation combinations.
ASLR (Address Space Layout Randomization) randomizes the load addresses of key process data regions (such as the stack, heap, and library base addresses), making it difficult for attackers to predict target addresses and thus raising the difficulty of exploiting memory corruption vulnerabilities. CFG (Control Flow Guard) validates whether the target address belongs to a legitimate function entry before indirect calls (such as virtual functions and function pointers), blocking the common path of control-flow hijacking. Both are mitigation measures that "increase exploitation uncertainty" rather than eliminating the vulnerability itself. Logic bugs do not rely on guessing memory layouts or hijacking control flow—attackers achieve their goals by abusing legitimate interfaces and state transitions, so these mitigations are essentially ineffective against them.
Full Chain Means Crossing Multiple Trust Boundaries
The so-called "Full Chain" typically refers to starting from the renderer process and ultimately breaking through the browser sandbox to affect the operating system. This path requires breaking through multiple isolation layers in sequence, with each stage relying on precise exploitation of Edge-specific logic flaws.
Modern browsers use a multi-process architecture: the renderer process is responsible for parsing and rendering untrusted web content and runs within a restricted sandbox; the browser main process holds higher privileges such as network, file, and UI access; and the operating system is the ultimate target. After the renderer process is compromised, attackers still need to break out of the sandbox (usually via logic flaws in IPC interfaces or kernel/system service vulnerabilities) to affect the host. The so-called "full chain" starts from code execution in the renderer process, breaches process isolation and sandbox boundaries layer by layer, and ultimately gains capabilities at the operating system level. Each boundary layer corresponds to an independent attack surface and exploitation technique, which is why full-chain research is considered high-value.
Research Value from Public Discussion
The appearance of this topic on Hacker News shows that such research has traction in the technical community. Although discussion热度 itself cannot be equated with vulnerability severity, it reflects the growing interest of security researchers in non-memory attack surfaces. For browser vendors, fixing logic vulnerabilities often involves functional refactoring, making cost and priority assessment more complex.
Business logic vulnerabilities and memory vulnerabilities have fundamentally different remediation patterns. Memory flaws can usually be resolved locally through bounds checking, compiler hardening, or patch-style fixes; logic vulnerabilities are often rooted in feature design and state management, and remediation may involve interface contract adjustments, permission model restructuring, or cross-process protocol changes, easily introducing compatibility risks and regression issues. Therefore, vendors must weigh the functional impact when scheduling fixes, and response cycles are typically longer. This also means that disclosure and coordinated remediation of logic vulnerabilities rely more on communication mechanisms between the research community and vendors.
Implications for Defenders
Relying solely on memory safety hardening is not enough to cover the entire attack surface. Browser vendors need to incorporate logic validation, cross-process permission boundaries, and state machine consistency into routine threat modeling processes. For security teams, focusing on anomalous paths formed by "legitimate operation sequences" may be more forward-looking than tracking individual memory errors.
Since the original material only provides the title and source information without disclosing specific vulnerability IDs, affected versions, or technical details, this analysis remains at the methodological level. Complete technical details require reference to the original research report.
Related articles

DeepSeek Harness: A Beginner's Installation and Testing Guide
A DeepSeek Harness tutorial for test engineers: set up Node.js, launch with one NPX command, configure official and third-party models, and explore web search, file I/O, and trace-view agent observability.
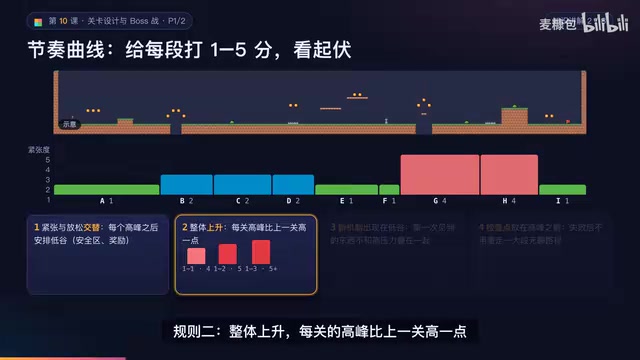
AI Game Development in Practice: Designing Levels with the Four-Step Method and Pacing Curves
AI game development lesson 10: design levels with the four-step method (teach, practice, combine, test) and a 1-5 pacing curve, plus sightline guidance and safety zones—implement Animatable Body 2D moving platforms and generate ASCII sketches for 1-2 Underground Cavern and 1-3 Guard Hall.
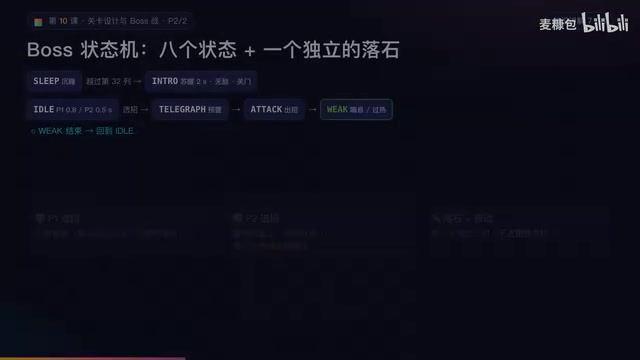
AI Game Development in Practice: Two-Phase Boss State Machines and Death Heatmap Tuning
AI game development lesson 10: implement a two-phase Boss with a state machine, guarantee fairness with color signals and a 0.4-second warning floor, locate difficulty cliffs with a death heatmap, and apply lightest-to-heaviest fixes one at a time, with an acceptance checklist and common pitfalls.