Entra to Stop Updating MemberOf Dynamic Groups: SCIM Provisioning Faces Silent Failure Risk

Entra memberOf-based dynamic groups will stop updating on November 3, 2026, and SCIM provisioning will fail silently.
Microsoft Entra has announced that dynamic groups based on memberOf rules will stop updating on November 3, 2026, meaning applications relying on these groups for SCIM provisioning will be unable to automatically sync events such as new employee onboarding, role changes, and offboarding deactivation. Because the failure triggers no error alerts, the provisioning chain breaks imperceptibly, and problems often surface only when users complain or security audits occur. The article recommends auditing memberOf-based dynamic groups early, rewriting them as rules based on user attributes or explicit membership lists, and adding business-level monitoring during migration, using account count comparisons instead of relying on platform error logs.
A change in Microsoft Entra is approaching: dynamic groups built on memberOf rules will stop updating on November 3, 2026. For applications that rely on these groups for SCIM provisioning, this means events such as new employee onboarding and role changes will no longer sync automatically to downstream systems—and the entire process will trigger no error alerts whatsoever.
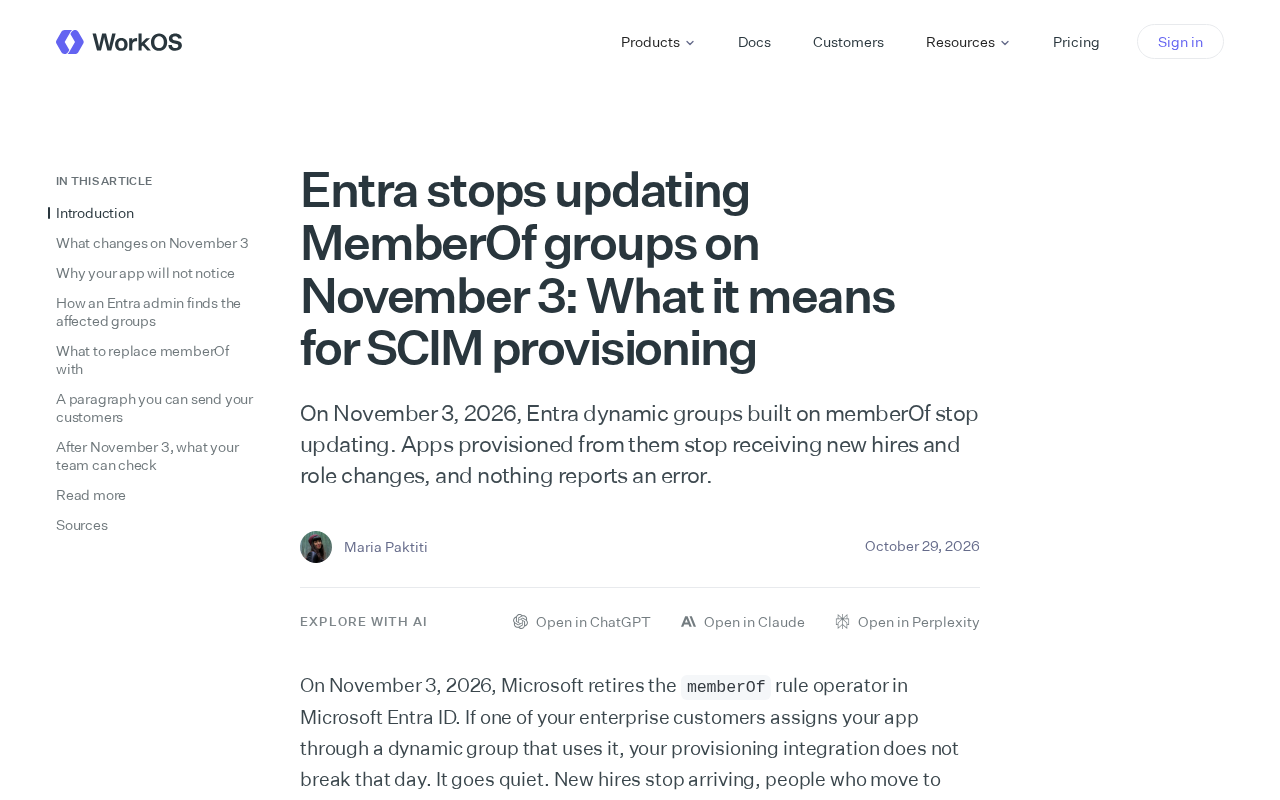
The Core of the Change: Dynamic Groups No Longer Respond to Membership Changes
Entra dynamic groups allow administrators to automatically maintain group membership lists using rule expressions, and the memberOf attribute has long been used to express nested logic such as "members of a certain group." Once rules stop updating, dynamic groups conditioned on memberOf will freeze at their current membership snapshot.
The problem is that this failure is silent. Entra won't throw exceptions, and no failure records will appear in the SCIM provisioning logs—applications simply stop receiving new provisioning events. For SaaS applications that use Entra groups as their permission source, new employees may not get accounts for a long time, and transferred employees' permissions won't update with their role changes.
How memberOf Rules Work
memberOf is the attribute used in Entra dynamic group rules to express nested membership relationships. When a rule is written like user.memberOf -any {value eq "groupID"}, Entra continuously computes the user's membership in the target group in the background and dynamically adds or removes group members accordingly. This secondary computation depends on real-time consistency of group relationships, so any change in upstream group membership triggers a recomputation of downstream dynamic groups. Once memberOf stops updating, dynamic groups lose their ability to perceive membership changes and freeze at the last successfully computed snapshot. Understanding this is key: what fails is not the group itself, but the portion of the group rule's computation logic that depends on membership relationships.
Specific Impact on the SCIM Provisioning Chain
The typical SCIM provisioning chain is: user/group changes in Entra → the provisioning service detects differences → it pushes create, update, or deactivate operations to downstream applications. When dynamic groups stop updating, the starting point of the chain is broken.
- New employee onboarding: After being added to a group based on memberOf rules, the group itself doesn't update, and downstream applications receive no create event.
- Role changes: Employee transfers trigger changes in group membership, but dynamic groups no longer reflect this change, and permission adjustments lag behind.
- Offboarding deactivation: Deactivation logic that likewise depends on group membership may fail, leaving security gaps.
You may not have noticed that this type of problem doesn't light up red on monitoring dashboards. Operations teams often only realize the provisioning chain has broken when users complain that "my account wasn't created" or when a security audit finds that "former employees' accounts are still active."
The SCIM Protocol and Provisioning Mechanism
SCIM (System for Cross-domain Identity Management) is a standard protocol for synchronizing user and group identities across systems. In Entra's provisioning service, it periodically scans for differences between the source directory and the target application, and pushes create, update, and deactivate operations to downstream applications as standard REST requests. The provisioning service determines whether "something has changed" based on whether the source object's attributes or group membership list have changed. Therefore, when a dynamic group no longer updates its membership list, the provisioning service considers "nothing happened" at the difference-detection stage and naturally generates no push requests. This is also why no failure records appear in the SCIM provisioning logs—the chain was never triggered at all, rather than erroring after being triggered.
Troubleshooting and Migration Recommendations
Faced with this change, administrators need to inventory the affected dynamic groups and provisioning configurations as early as possible.
The first step is to identify the scope of dependencies. Check the groups referenced in all SCIM provisioning configurations and confirm which dynamic groups' rule expressions use memberOf. These groups are where the risk exposure lies.
The second step is to rewrite the rule logic. Change nested rules based on memberOf to rules based directly on user attributes (such as department, job title, or cost center) or explicit membership lists. Direct-attribute rules do not depend on secondary computation of group membership and are more stable.
The third step is to add monitoring. Before migration is complete, add business-level monitoring for critical provisioning chains—for example, periodically compare the actual number of accounts in downstream applications with the number of people that should be provisioned on the Entra side, using discrepancy alerts instead of relying on platform error logs.
Direct-Attribute Rules and Explicit Membership Lists
Direct-attribute rules refer to dynamic group rules that directly reference attributes of the user object itself (such as department, jobTitle, costCenter), without secondary computation via group relationships. The stability of such rules comes from their single data source: as long as user attributes are maintained correctly, the rule results are deterministic. Explicit membership lists are static member sets maintained manually or through automation scripts, with no dependence on the rule engine at all. Each approach has trade-offs: direct-attribute rules suit scenarios automated along organizational dimensions, while explicit lists suit privileged groups with small membership and infrequent changes. During migration, prioritize converting critical provisioning chains to direct-attribute rules, and for logic that cannot be expressed with attributes, consider explicit lists with automated maintenance.
Why Silent Failure Is More Dangerous
The hardest thing to handle in infrastructure changes is "breaking without erroring." Explicit errors trigger alerts, tickets, and on-call responses; silent failures hide the fault on the business side, and by the time it surfaces on its own, impact has often accumulated over time.
The time window for this Entra change is clear, but the real risk is whether organizations realize they depend on a capability that is about to fail. For teams using SCIM provisioning, it's worth doing a group rule audit now and cleaning up memberOf dependencies thoroughly—rather than waiting until after November 3 to discover problems through user feedback.
Original title: Entra stops updating MemberOf groups on November 3: What it means for SCIM provisioning
One-line Summary
Entra dynamic groups based on memberOf will stop updating on November 3, 2026, and SCIM provisioning will fail silently.
Paragraph Summary
Microsoft Entra has announced that dynamic groups based on memberOf rules will stop updating on November 3, 2026, meaning applications relying on these groups for SCIM provisioning will be unable to automatically sync events such as new employee onboarding, role changes, and offboarding deactivation. Because the failure process triggers no error alerts, the provisioning chain will break imperceptibly, and problems often only surface when users complain or security audits occur. The article recommends that administrators audit dynamic groups using memberOf rules as early as possible, rewrite them as rules based on user attributes or explicit membership lists, and add business-level monitoring during migration, using account count comparisons instead of relying on platform error logs.
Related articles

Cursor AI in Practice: Weighing Efficiency Gains Against Costs in an AI IDE
An in-depth look at Cursor AI IDE's interface layout, four modes (Agent/Plan/Debug/Ask), model selection, and Git context integration, with hands-on demos weighing subscription costs against going direct to Claude.
Free Landing Page Design Rules Library: A Practical Guide for Claude Code and Cursor
A free landing page design skill for Claude Code and Cursor: MIT licensed, nearly 9,000 stars, asks about offer/audience/action before planning 12 sections with hard font and spacing constraints.
Cursor Keeps Writing Wrong Code? The Problem May Be Context, Not Prompts
Cursor keeps writing wrong code? The problem may be context, not prompts. Learn how to supply relevant files, full error messages, and expected results, plus a plan-first, small-step, test-driven workflow to reduce AI coding errors—while remembering code review remains the developer's job.