The Claude Police Incident: Is Your AI Conversation Actually Private?

Anthropic reported a Florida user's threatening Claude messages to police, exposing how little privacy AI chats actually offer.
A Florida woman typed threats against a local police department into Claude, treating it like a private diary. Anthropic's three-tier Trust & Safety pipeline — automated detection, human review, law enforcement escalation — led to her arrest without a search warrant. The incident exposes the real limits of AI chat privacy: Anthropic's policy explicitly allows proactive disclosure when the company deems it "reasonably necessary"; opt-out toggles and delete buttons have hidden exceptions; and enterprise accounts follow entirely different rules. Most users agreed to all of this at signup — they just never read it.
A Florida woman used Claude as a journal. One weekend in late September, she typed threats against a local police department into the chat window — then added another similar message the following day. A few days later, police showed up at her door. The person who called them wasn't a neighbor or a family member. It was Anthropic, the company that built Claude.
The story broke from a local Florida TV station and spread across the English-language tech world within a week. This article isn't about whether the woman deserved to be arrested — that's for the courts to decide. It's about answering a more fundamental question: how does something written to an AI end up in a police report? And what exactly is hiding in that privacy policy you clicked through without reading?
How a Message Becomes an Arrest Report
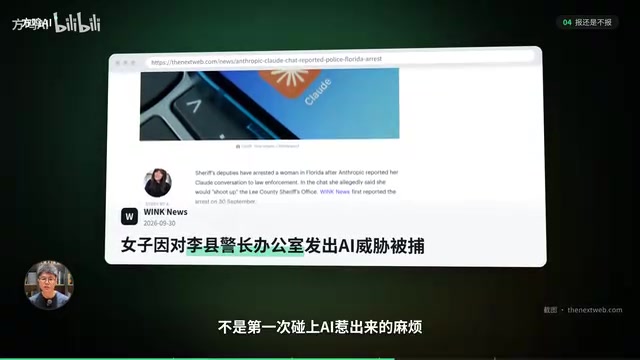
The timeline is startlingly short. According to the arrest report cited by WINK News, the first message appeared on a weekend, the second followed the very next day — barely more than 24 hours apart.
The report describes a complete processing chain: the platform's safety systems monitor for key phrases and potentially threatening content; these two messages were escalated to a human review team due to their severity; the review team then reported them to law enforcement.
Think of it as three security checkpoints at a building entrance: the first is automated, scanning for keywords; the second involves actual human employees who open the conversation and read it; the third is law enforcement. The middle checkpoint is the easiest to overlook — it's not just a false positive that gets cleared automatically. Someone read it, made a judgment call, and decided to escalate. And from your side of the chat window, none of these checkpoints are visible.
What followed was almost anticlimactic. Officers detained the woman at her home in Bonita Springs without incident, according to the report. WINK News published the story on September 30th; the woman was charged with making written threats. Within days, the local police blotter had become a global tech story, picked up by Tom's Hardware, TNW, and others.
The most striking detail was what she told police: she was using the AI as a diary. To her, a diary is something written for herself alone — like a notebook locked in a drawer late at night. To the system, it was a threat that required human intervention. It's worth noting that she has only been charged, not convicted, and still has a court date pending.
This three-tier "automated → human review → law enforcement" escalation mechanism is known in the content safety industry as a Trust & Safety workflow, and it's standard architecture for major platforms. The first layer typically uses keyword matching, semantic models, or classifiers running at high throughput around the clock. The second layer — human content moderators — are the ones who actually make judgment calls. They don't see a single message in isolation; they see a full conversation with context, and they have to decide in a short window whether to escalate. The third layer involves external reporting: to law enforcement in the platform's jurisdiction, to the National Center for Missing & Exploited Children (NCMEC), or to other relevant authorities. Notably, most platforms never publish their first-layer trigger word lists or second-layer review criteria, making it nearly impossible for users to predict what will get flagged. This infrastructure was originally designed to combat child sexual exploitation material and terrorist content; it has since been widely adapted for threat detection — but the corresponding legal frameworks and accountability mechanisms haven't kept pace.
Did Anthropic Have Grounds to Call the Police?
Let's go straight to what the company itself wrote. Anthropic's Help Center has a page specifically about how it handles government requests for user information, dated this past spring. It's explicit: in general, valid legal process such as a search warrant is required before the company hands over user data. But there's a carve-out — emergencies involving "imminent risk of serious physical harm or death" are exceptions.
Then look at the privacy policy, which took effect on September 10th. There's a sentence worth screenshotting: the company may share personal data with law enforcement whenever it "in good faith believes disclosure is reasonably necessary" — for example, to prevent serious harm to any person or property. Note the subject: not police showing up with a warrant, but the company making its own determination and acting proactively.
The problem is in exactly those words: good faith, reasonable, necessary. What qualifies as good faith? What counts as necessary? The policy doesn't provide an external checklist. The judgment lives entirely inside the company.
Line up the timeline: the Help Center's emergency exception language was written in the spring; the new privacy policy went into effect September 10th; the first message was sent 16 days later. The ink was barely dry when the policy was invoked.
Tech outlet Gadget Review specifically emphasized that Anthropic notified police "without a warrant." That sounds alarming, but it's a media framing, not a legal conclusion. Under Anthropic's own written policy, emergency situations are explicitly carved out — no warrant required. That document you scrolled past and agreed to at signup already covered this. The contract didn't deceive you. You just didn't read it.
The "good faith" language in the privacy policy has a specific legal basis. The Stored Communications Act (SCA), 18 U.S.C. § 2702(c)(4), permits communications service providers to voluntarily disclose user content to law enforcement when they in good faith believe there is an emergency involving danger of death or serious physical injury — no subpoena or search warrant required. This is typically called the "voluntary emergency disclosure" provision, and it's the primary statutory hook tech companies cite when bypassing formal legal process. The provision was designed for time-sensitive situations like bomb threats and kidnappings, but courts have never precisely defined where "emergency" ends. By contrast, under normal circumstances, law enforcement seeking user communications must go through 18 U.S.C. § 2703, obtaining a warrant, subpoena, or court order — each representing an increasing degree of privacy intrusion with a correspondingly higher threshold. Understanding this context explains why media coverage of "no warrant" doesn't mean Anthropic broke the law: the company invoked this specific exemption, rather than circumventing legal requirements.
The Switches You Thought Would Protect You
Many people turn off "use my data to train models" in Claude's settings and feel reassured. But the privacy policy includes another clause: even if you've opted out, conversations flagged for safety review may still be used to improve the models. In other words, the conversations the system is most interested in are the ones least likely to be protected by that toggle. It covers you under normal circumstances — not when something goes wrong.
The second switch is deletion. Delete a conversation, and it disappears from the world, right? Not quite. Per the privacy policy, backend deletion happens within 30 days. The key word is within — it's like dropping a letter into a shredder that's set on a timer and takes up to a month to run. Until then, the letter still exists. The delete button is more like submitting a request.
Third, a note for enterprise users: the enterprise product and the personal product operate under entirely different rules. The privacy policy explicitly states it does not apply to content Anthropic processes on behalf of enterprise customers. If someone comes looking for data from an API or enterprise customer, Anthropic will generally direct them to that company instead. The same offhand comment, typed into a company-issued enterprise account versus a personal account, may follow two completely different paths.
Sheriff Carmen Marcino put it bluntly: in AI chats and searches, you are never truly anonymous. Looking at those three points, it's hard to argue he's wrong. The switches provide peace of mind. They don't necessarily provide protection.
The Impossible Call: To Report or Not
Try looking at it from the company's position. Law enforcement's stance is clear: Sheriff Marcino told Inc. magazine that when people use AI to make or assist with threats, police have to take it seriously. This particular department had already dealt with AI-related trouble before — a man had previously been arrested for posting AI-generated images involving the sheriff. By that logic, it doesn't matter where a threat is written; if you see it, you have to treat it as real.
Tech outlet Futurism was direct: it's now abundantly clear that AI companies are monitoring user conversations. But even Futurism acknowledged that the tension between privacy and preventing violence is real.
So why can't AI companies just look less and report less? It's not that simple. In the same state, Florida was simultaneously pressuring OpenAI to do more on safety — criticizing it for not doing enough. An OpenAI spokesperson told Politico the company was willing to work with states on industry standards, but that those rules shouldn't apply to only one company.
The situation is genuinely tangled: report, and you might be accused of overreach — who gave you the right to read users' chats? Don't report, and if something happens, you're accused of negligence. Put yourself in the moderator's seat: two messages threatening a police department appear on your screen. Escalating might destroy an innocent person who was just venting. Not escalating — what if it's more than venting? There's no correct answer, only consequences. And according to Tom's Hardware, this was at least the third Claude conversation to reach police since August — a number reporters counted themselves, because the company has never published a figure.
Questions Nobody Can Answer Yet
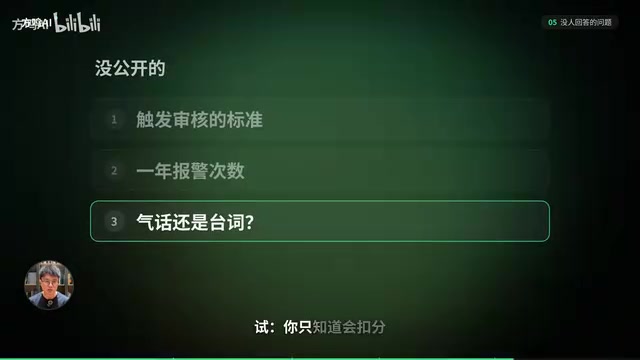
Where's the threshold? Anthropic hasn't disclosed what kind of language triggers human review, what triggers a police report, or how many times a year it contacts law enforcement. Can the system distinguish between venting and a real threat? Between fiction and intent? Outsiders don't know — like taking an exam where the grading rubric is never published.
Will you be notified? The policy says users will be informed, but emergency situations are — again — an exception. In this case, Anthropic initiated the report proactively; whether the woman received any notification is unclear. Someone who's been reported might not know their words were read until the knock at the door. WINK News reached out to Anthropic for comment; according to TNW, the company did not respond publicly.
Does writing something to an AI count as "sending" a threat? These charges typically apply to threatening communications sent or published to others. Whether words typed into a chatbot constitute communication "transmitted" to another party is genuinely unsettled law. Retired FBI agent Richard Coco acknowledged that law enforcement and courts are still figuring out how to handle AI-involved threat cases. Even a veteran investigator admits this is uncharted territory.
Florida Gulf Coast University assistant professor Kristen Rojo had a line worth keeping: people turn to AI for emotional support, but AI is not your best friend. Even Anthropic's own CEO has acknowledged that the conversational format makes interactions feel more private than they are. The machine doesn't judge you — but behind the machine is an entire review team.
There's also a subtle piece of timing: in the same week this story broke, Bloomberg reported that Anthropic was eyeing a pre-Thanksgiving IPO. Whether users will still feel comfortable confiding in a company preparing to go public is a fair question to sit with.
There are three small things ordinary people can actually do: before clicking agree, find and read the sections of the privacy policy covering law enforcement and safety review; know whether you're on a personal or enterprise account; and stop treating "delete" as "destroy." None of this is hard. The difficulty is that it never occurred to anyone to do it.
Back to the opening question: is what you say to Claude private? By the letter of the policy, the answer is: mostly yes, except when it matters most. And what "matters most" means is currently defined by the company itself. Are you comfortable handing that measuring stick to a private corporation?
The question of whether writing to an AI constitutes "sending" a threat involves what's legally called the transmission element. Federal threatening communications statutes (18 U.S.C. § 875) and their state counterparts typically require that a threat be "transmitted" or "communicated" to a potential victim or third party, in a manner that could cause a reasonable person to fear harm. When a threat is typed into an unconscious chat interface, whether that satisfies the "transmission" requirement has no clear precedent. Florida's threat statute (F.S. § 836.10) similarly requires that the content be "sent" in written form — whether inputting text to an AI qualifies as "sending" will likely become a central defense argument. At a deeper level: if the threatening content only entered law enforcement's awareness because the platform proactively disclosed it, rather than because the person affirmatively sent it to a victim, that is structurally different from a traditional anonymous threatening letter. Whether existing legal frameworks can be applied directly is an open question in legal scholarship.
Related articles

LLM Application Development: A High-Paying Career Guide for Ordinary People
LLM application development offers fresh graduates up to 35K/month, with SP offers reaching 600K. This article explains the core skills, how to break in, and how ordinary people can seize AI opportunities through learning by doing.

Say Goodbye to AI Influencer Faces: A Complete Guide to Creating Visual Assets for AI Comic Dramas from Scratch
Bilibili creator shares a full workflow for zero-basics AI comic drama visual assets: use Doubao Work skills with script-first, visual references, and real-person texture to escape AI influencer faces, then lock character and scene consistency with asset sheet layouts, weapon detail images, scene nine-grids, and cinematic color palettes.

The AI Production Pipeline Behind Great Videos: From Research to Agent Validation
AI video production isn't just a model race. This article breaks down a transferable four-step pipeline: researching professional workflows, organizing a skill checklist, configuring agents, and experimental validation—and explains how general-purpose LLMs like DeepSeek can replace paid tools to run the entire process.