Vercel MCP Opens Access: Replacing Manual Review with CIMD
Vercel MCP removes manual review, using CIMD so clients self-declare identity and trust shifts to user judgment.
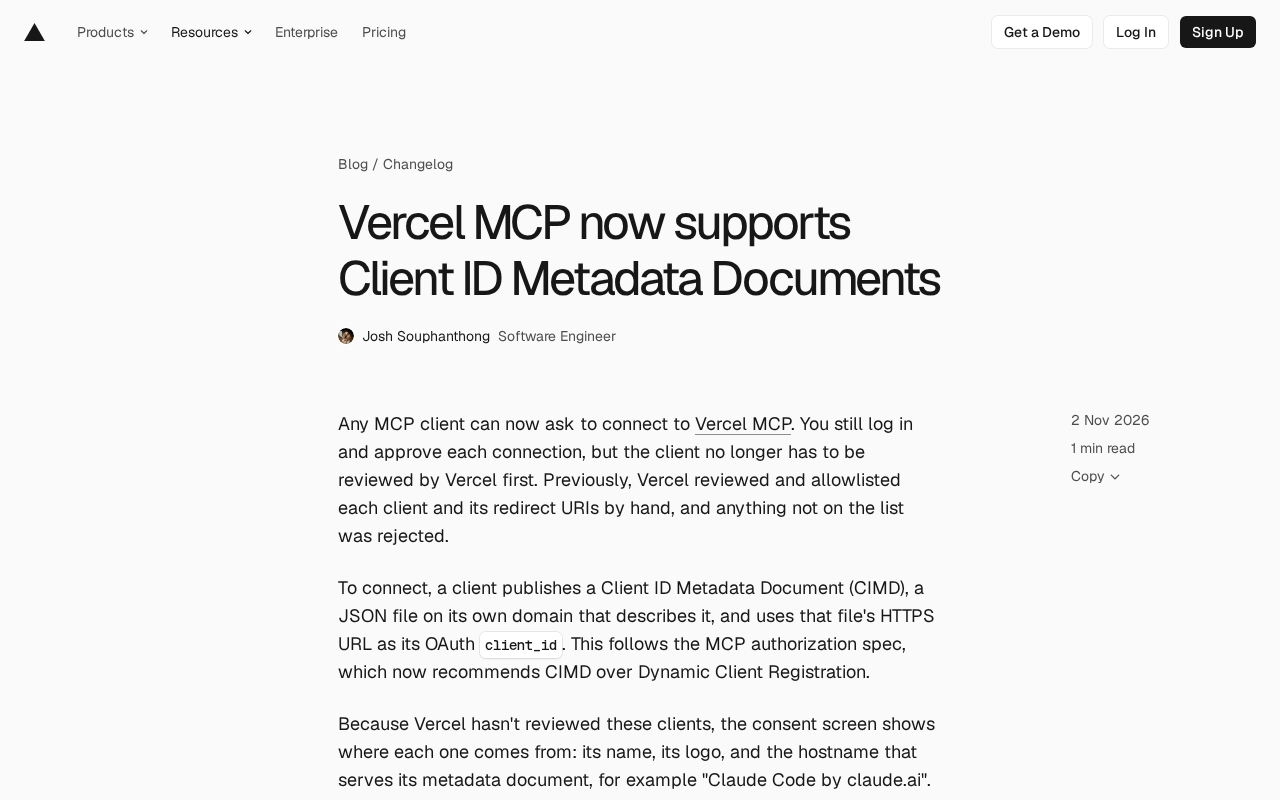
Vercel's MCP service has removed manual review and allowlisting for each connecting client and redirect URI; any MCP client can now request a connection. Clients publish a Client ID Metadata Document (CIMD) JSON file on their own domain and use its HTTPS URL as the OAuth client_id to declare identity. This follows the MCP authorization spec's latest recommendation to use CIMD instead of Dynamic Client Registration. The trust model shifts: the OAuth consent screen shows the client name, logo, and hostname but no Vercel verified badge, so users must judge hostname trust themselves. Registered apps are unaffected, and users still log in and approve each connection. This lowers the barrier to entry and offers MCP service providers a reference template for balancing openness and security.
Title
Vercel MCP Opens Access: Replacing Manual Review with CIMD
Meta Description
Vercel MCP now supports Client ID Metadata Documents, allowing any MCP client to request a connection without manual review. This article explains how CIMD works, how trust is displayed on the consent screen, and the impact on open access in the MCP ecosystem.
Article Content
Vercel's MCP service recently underwent a key change: any MCP client can now request to connect to Vercel MCP, without the Vercel team manually reviewing and whitelisting it. Instead, clients declare their identity by publishing a Client ID Metadata Document (CIMD). This adjustment follows the latest recommendations of the MCP authorization specification and provides a new reference model for open access in the MCP ecosystem.
From Manual Review to Self-Declaration: How CIMD Works
In the past, Vercel manually reviewed and managed an allowlist for every MCP client that wanted to connect, along with its redirect URI, and any client not on the list was rejected. This model was secure but had limited scalability—especially as the number of MCP clients grew rapidly, the review process became a bottleneck for access.
Now, clients only need to publish a JSON file on their own domain—the Client ID Metadata Document—describing their own information, and use that file's HTTPS URL as the OAuth client_id. Vercel no longer pre-reviews these clients, but instead relies on the metadata provided in the CIMD to identify the source of the request. This follows the MCP authorization specification, which currently recommends using CIMD instead of Dynamic Client Registration.
Dynamic Client Registration (DCR) is an extension specification of OAuth 2.0 (RFC 7591) that allows clients to automatically register themselves with an authorization server at runtime and obtain a client_id without manual intervention. MCP adopted this mechanism early on to support a large number of unpredictable clients. However, DCR has obvious drawbacks: anyone can register any number of clients at will, making it difficult for authorization servers to trace the client's true identity and easy for the mechanism to be abused; at the same time, there is no verifiable binding relationship between the registration information and the client's actual operator. The core improvement of CIMD is that it turns the client_id itself into an HTTPS URL pointing to a metadata document hosted on the client's own domain—the client must host the document on its own domain, thereby establishing a verifiable association at the URL level of "who is declaring the identity." The authorization server does not need to maintain a registration database; it only needs to fetch the document by URL to obtain information such as the client name, logo, and redirect URI.
Changes in the Trust Model: You Can See Who Is Requesting
After the review step was removed, the foundation of trust shifted. Because Vercel does not review these clients, the OAuth consent screen clearly displays the source information of each client: name, logo, and the hostname providing the metadata document. For example, the screen might display "Claude Code by claude.ai."
These CIMD clients do not receive Vercel's verified badge, so when users approve a connection, what they really need to trust is that hostname. In other words, Vercel partially transfers the responsibility of judging whether a client is trustworthy to the user, while assisting decision-making by displaying source information. The consent screen also lists the permissions the client will receive, a team selector, and cancel and allow access buttons.
For applications already registered with Vercel, this change has no impact; they remain in their original state.
The OAuth consent screen is a key interaction step in the OAuth authorization code flow: when a client requests access to user resources, the authorization server displays a page showing "which application, where it comes from, and which permissions it requests," and the user decides whether to authorize. Under the traditional manual review model, the application information on the consent screen was verified by the platform, and users trusted the platform's endorsement; under the CIMD model, this information is self-declared by the client, and the platform no longer guarantees its authenticity. Therefore, the consent screen changes from a trust signal of "platform-reviewed" to a decision interface where "users judge the source themselves." By displaying the hostname and not granting a verified badge, Vercel makes this trust shift clear: the hostname becomes the only objective identifier users can rely on, and users need to judge for themselves whether the domain is trustworthy.
Potential Impact on the MCP Ecosystem
This change by Vercel is consistent with the evolution direction of the MCP authorization specification. CIMD allows clients to independently declare their identity, reduces the manual management cost for service providers, and makes it easier for new clients to connect. For developers who want to quickly integrate Vercel capabilities, the barrier to entry is significantly lowered.
However, open access also means that security boundaries need to be re-examined. Users need to develop the habit of checking the hostname on the consent screen rather than relying on the platform's prior review. By displaying the client source and explicitly not providing a verified badge, Vercel draws a clear boundary of responsibility.
For MCP service providers, Vercel's approach provides a reference template: replace manual review with standardized metadata documents while ensuring users are informed, seeking a balance between openness and security. Client developers, in turn, need to ensure that their CIMD files are accurate, accessible, and have clearly identifiable hostnames.
The MCP authorization specification is the section of the Model Context Protocol that defines how clients securely obtain access tokens, based on OAuth 2.1. The specification requires MCP clients to follow the standard OAuth flow when connecting to remote servers in order to obtain user authorization and carry tokens when accessing resources. Because MCP clients come in many forms (IDE plugins, CLI tools, desktop applications, agent frameworks, etc.), the specification initially recommended DCR to support dynamic registration; however, as the ecosystem expanded, the problems of DCR abuse and untraceable identity became prominent, and the specification shifted to recommending CIMD. This evolution means that MCP's authorization model is moving from "registration equals trust" to "verifiable declaration," with service providers judging the source based on client self-hosted metadata rather than relying on centralized registration review. Understanding this specification background helps clarify why Vercel's change is regarded as a bellwether for ecosystem trends.
How to Connect
Any MCP client can request to connect to Vercel MCP. Users still need to log in and approve each connection, but the client itself no longer needs to go through Vercel's pre-review. For specific connection instructions, refer to the Vercel MCP documentation.
This update may appear to be merely a technical adjustment to the authorization flow, but in fact it reflects a trend in the MCP ecosystem from closed review toward open declaration. When the number of clients grows beyond what manual review can cover, a trust mechanism based on standardized metadata becomes the more realistic choice.
One-line Summary
Vercel MCP removes manual review and uses CIMD to let clients self-declare their identity, shifting trust to user judgment.
Paragraph Summary
Vercel's MCP service has removed the previous manual review and allowlist management for each connecting client and redirect URI. Any MCP client can now request a connection. Clients only need to publish a Client ID Metadata Document (CIMD) JSON file on their own domain and use that file's HTTPS URL as the OAuth client_id to declare their identity. This approach follows the latest recommendation of the MCP authorization specification—using CIMD instead of Dynamic Client Registration. The trust model changes accordingly: the OAuth consent screen displays the client name, logo, and hostname, but does not provide a Vercel verified badge, so users must judge for themselves whether the hostname is trustworthy. Registered applications are unaffected, and users still must log in and approve each connection. This change lowers the barrier to entry and provides MCP service providers with a reference template for balancing open access and security.
Related articles
Skykea Showdown: A Hilarious Variety Show Experience of a Minecraft Airship Building Competition
Skykea Showdown is a Minecraft airship building racing variety show. This article analyzes its two-phase build + hole race format, airship mod lift physics, secret mission design, and team confrontation dynamics—ideal for game content creators.
Did the US Midterms Vote No to AI Data Centers? A Map Reveals the Truth
After the US midterms, media claimed voters rejected AI data centers, but a map shows restrictive votes are concentrated in a few Ohio townships, affecting less than 1% of US towns—the national anti-AI wave is exaggerated.
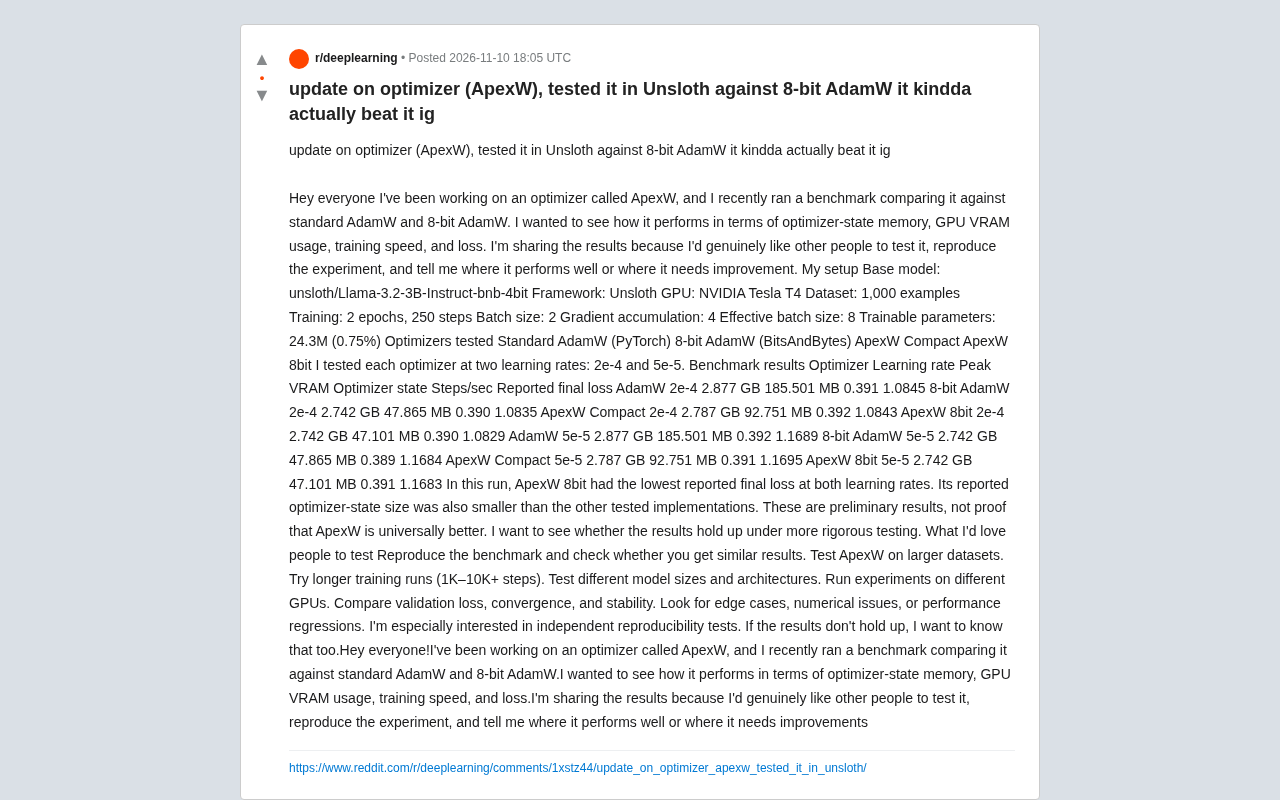
ApexW Optimizer Benchmark: Matches 8-bit AdamW in Unsloth with Lower Memory Usage
Developer shares benchmark of ApexW optimizer in Unsloth: ApexW 8bit has lower optimizer state memory (47.101 MB) and slightly better final loss than 8-bit AdamW, but similar speed. Needs independent reproduction.