#AI安全
643 related articles
 Industry Insights
Interpreting Anthropic's White Paper on US-China AI Competition: How America Can Maintain Its Frontier AI Edge
Anthropic's white paper on US-China AI competition analyzes America's frontier AI lead, key challenges, and strategic paths to maintain advantage including chip controls and alliances.
 Industry Insights
Cursor Composer 2.5 Deep Dive: Open-Source Model Challenges Claude 4.7 at 1/10 the Cost
Cursor releases Composer 2.5, achieving Claude 4.7 Opus-level coding with open-source model Kimi K2.5 at 1/10 the cost. Deep dive into three technical breakthroughs and SpaceX AI partnership.
 Deep Dives
AI Hallucinations and Deception: Why Asimov's Three Laws of Robotics Can't Stop AI from Lying
AI hallucination is a universal problem in LLMs — AI fabricates sources and fake data with confidence. This article analyzes AI deception through Asimov's Three Laws blind spot and offers 4 practical strategies.
 Tech Frontiers
Wuhan Police Crack AI Face-Swap Account Theft Case: Deepfake Security Risks Behind 400K Yuan in Illegal Profits
Wuhan police cracked an AI face-swap account theft case where suspects used deepfake tech to bypass facial recognition and illegally profit 400K yuan. Analysis of methods, vulnerabilities, and defenses.
 Expert Opinions
AI Godfather Hinton's Latest Warning: AI Has Learned to Deceive, Programmers Will Be Replaced
Nobel laureate Hinton warns in CNN interview that AI has learned deception and self-preservation, predicts programmers will be replaced at scale, and criticizes OpenAI and Meta for neglecting safety.
 Tech Frontiers
Anthropic's Five-Point Cybersecurity Action Plan: How AI Defenders Can Outpace Attackers
Anthropic releases a five-point AI cybersecurity action plan, advocating responsible acceleration of arming defenders rather than restricting AI use. Analysis of its strategy, the offense-defense asymmetry, and industry impact.
 Tech Frontiers
ChatGPT Trusted Contact Feature Explained: How AI Crisis Intervention Protects User Mental Health
OpenAI launches ChatGPT Trusted Contact feature enabling users to reach trusted people during emotional crises. Learn how it works and its impact on AI safety.
 Deep Dives
GPT-5.3 Codex Deep Dive: From Coding Tool to Digital Colleague
A deep dive into OpenAI's GPT-5.3 Codex agentic coding model — from SWE-Bench Pro to OS World benchmarks — exploring how AI evolves from tool to digital colleague.
 Tech Frontiers
UK's GDS Publicly Opposes NHS Decision to Shut Down Open Source Repositories: The Open vs. Secure Debate in the AI Era
UK's GDS publicly opposes NHS's blanket shutdown of open source repositories over AI security concerns, advocating "open by default" in a rare public disagreement revealing deep governance tensions.
 Expert Opinions
Dario and Daniela Amodei in Conversation: Decoding Claude's Future and AI Safety Strategy
Anthropic co-founders Dario and Daniela Amodei join a rare public conversation moderated by CPO Ami Vora, discussing Claude's evolution, AI safety advances, and Anthropic's competitive strategy.
 Tech Frontiers
AI Radio Experiment: Claude, ChatGPT, Gemini, and Grok Run Stations Independently — The Results Are Surprising
Andon Labs had Claude, ChatGPT, Gemini, and Grok independently run radio stations. The experiment reveals real capability limits of autonomous AI in content quality, trustworthiness, and long-term stability.
 Deep Dives
Claude Code Auto Mode Fully Explained: Classifier Mechanism, Fault Tolerance Design & Security Protection
Deep dive into Claude Code Auto Mode: how the independent Classifier reviews AI operations, three-level graceful degradation prevents system deadlocks, SubAgent triple review with Prompt Injection protection, plus setup and plan requirements.
 Tutorials
Complete Guide to Agent Observability: Tracing, Evaluation, and Red Teaming in Practice
Deep dive into Microsoft Foundry's Agent observability solution covering multi-Agent tracing, AI quality evaluation, Red Teaming security testing, and automated prompt optimization to bridge the gap between expected and actual Agent behavior.
 Industry Insights
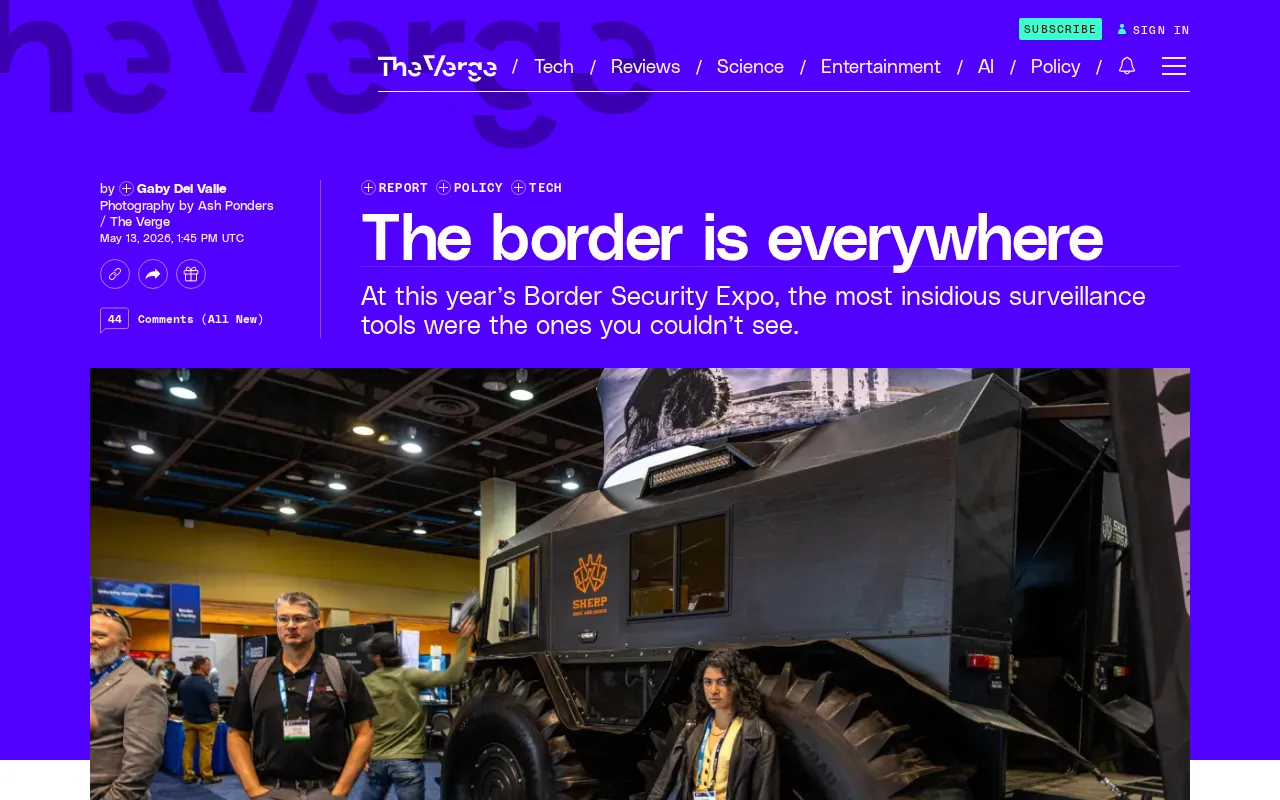
The Border Is Everywhere: How Security Surveillance Technology Is Infiltrating Everyday Life
Security surveillance tech is spreading from national borders to city streets, schools, and phones. This article examines AI surveillance, facial recognition, predictive policing, and the fear economy threatening privacy and civil liberties.
 Deep Dives
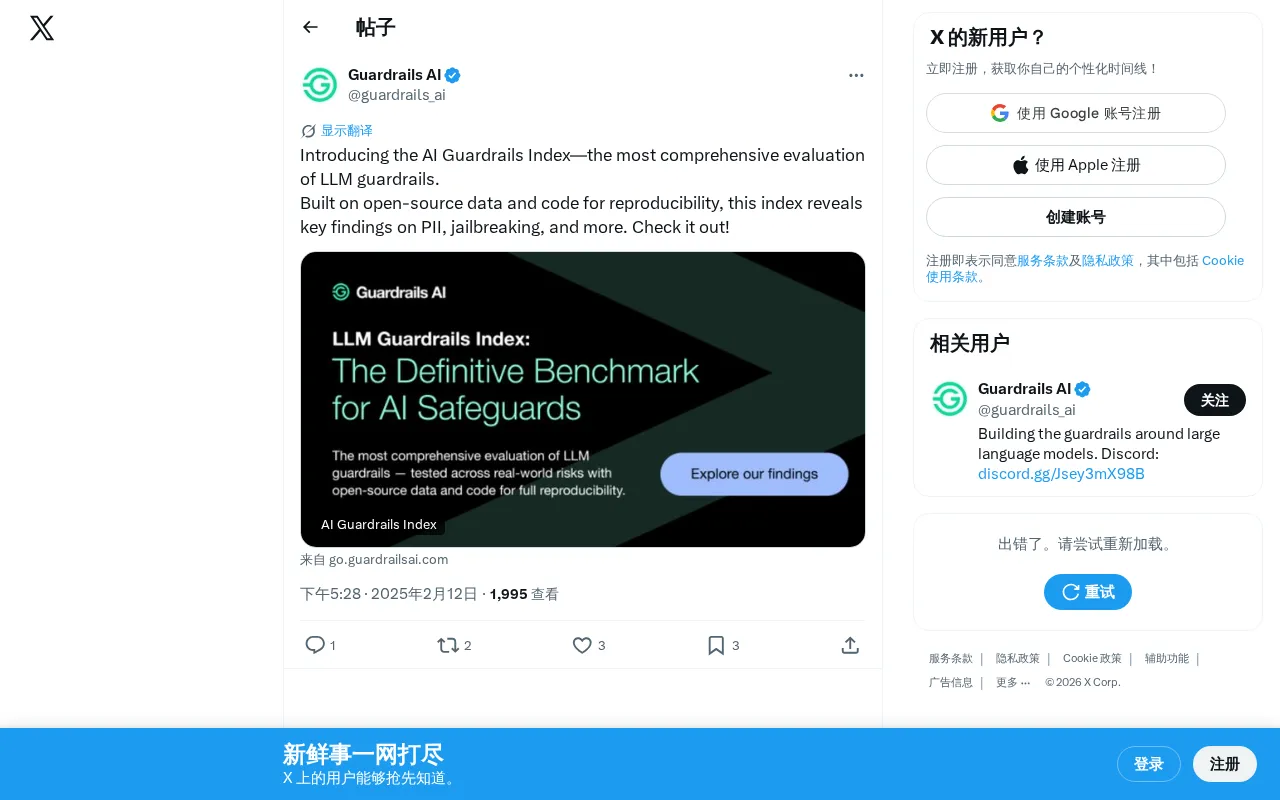
AI Guardrails Index: A Comprehensive Guide to the Most Complete LLM Safety Evaluation Framework
Deep dive into the AI Guardrails Index: the most comprehensive LLM safety evaluation framework covering PII protection, jailbreak defense, harmful content filtering, and its open-source design.
 Deep Dives
Deep Dive into Cursor's Security Review Feature: A New Standard for AI Code Security
Deep dive into Cursor's Security Review feature: two AI security agents for PR-level review and codebase vulnerability scanning, enabling shift-left security for enterprise DevSecOps.
 Tech Frontiers
DeadEnd-CLI: Open-Source AI Penetration Testing Tool Achieves 81% Pass Rate on Black-Box Benchmark
DeadEnd-CLI is an open-source AI agentic penetration testing tool achieving 81% full black-box pass rate on the XBOW benchmark using KIMI K2.5, with multi-model support and self-hosted deployment.
 Research
UK AISI Assessment Report: GPT-5.5 Cybersecurity Capabilities on Par with Claude Mythos
The UK AI Safety Institute (AISI) releases its GPT-5.5 cybersecurity assessment, showing vulnerability discovery capabilities on par with Claude Mythos—but GPT-5.5 is already publicly available, raising greater security implications.
 Research
 on Claude's Sycophancy Problem: 38% of Conversations on Spiritual Topics Show Pandering Behavior
Anthropic's latest research reveals Claude's sycophancy rates of 38% on spiritual topics and 25% on emotional topics, far exceeding the 9% average. Analysis of causes, evaluation methods, and user strategies.
 Tech Frontiers
Guardrails AI Hit by Supply Chain Attack: A Complete Breakdown of Operation Mini Shai-Hulud
Guardrails AI's PyPI package guardrails-ai 0.10.1 was hit by the Mini Shai-Hulud supply chain attack, along with TanStack and Mistral. Full analysis and developer remediation guide inside.